A distributed vulnerability database for Open Source
An open, precise, and distributed approach to producing and consuming vulnerability information for open source.
Ecosystems
- AlmaLinux
- 6608 View AlmaLinux vulnerabilities
- Alpaquita
- 17693 View Alpaquita vulnerabilities
- Alpine
- 10792 View Alpine vulnerabilities
- Android
- 4071 View Android vulnerabilities
- Azure Linux
- 20672 View Azure Linux vulnerabilities
- BellSoft Hardened Containers
- 963 View BellSoft Hardened Containers vulnerabilities
- Bitnami
- 10023 View Bitnami vulnerabilities
- Chainguard
- 1305241 View Chainguard vulnerabilities
- CleanStart
- 17870 View CleanStart vulnerabilities
- crates.io
- 3024 View crates.io vulnerabilities
- Debian
- 73779 View Debian vulnerabilities
- Docker Hardened Images
- 3479 View Docker Hardened Images vulnerabilities
- Echo
- 8246 View Echo vulnerabilities
- GIT
- 119974 View GIT vulnerabilities
- GitHub Actions
- 63 View GitHub Actions vulnerabilities
- Go
- 9776 View Go vulnerabilities
- Hackage
- 38 View Hackage vulnerabilities
- Hex
- 436 View Hex vulnerabilities
- Julia
- 1713 View Julia vulnerabilities
- Linux
- 31104 View Linux vulnerabilities
- Mageia
- 6364 View Mageia vulnerabilities
- Maven
- 7135 View Maven vulnerabilities
- MinimOS
- 185034 View MinimOS vulnerabilities
- npm
- 231807 View npm vulnerabilities
- NuGet
- 1957 View NuGet vulnerabilities
- opam
- 36 View opam vulnerabilities
- openEuler
- 9532 View openEuler vulnerabilities
- openSUSE
- 15354 View openSUSE vulnerabilities
- OSS-Fuzz
- 4063 View OSS-Fuzz vulnerabilities
- Packagist
- 7301 View Packagist vulnerabilities
- PyPI
- 26313 View PyPI vulnerabilities
- Red Hat
- 24908 View Red Hat vulnerabilities
- Red Hat Lightwell
- 288 View Red Hat Lightwell vulnerabilities
- Rocky Linux
- 5014 View Rocky Linux vulnerabilities
- Root
- 20269 View Root vulnerabilities
- RubyGems
- 5463 View RubyGems vulnerabilities
- SUSE
- 24519 View SUSE vulnerabilities
- SwiftURL
- 61 View SwiftURL vulnerabilities
- TuxCare
- 23663 View TuxCare vulnerabilities
- Ubuntu
- 70741 View Ubuntu vulnerabilities
- Wolfi
- 332055 View Wolfi vulnerabilities
OSV schema
All advisories in this database use the OpenSSF OSV format, which was developed in collaboration with open source communities.
The OSV schema provides a human and machine readable data format to describe vulnerabilities in a way that precisely maps to open source package versions or commit hashes.
{
  "schema_version": "1.7.4",
  "id": "GHSA-c3g4-w6cv-6v7h",
  "modified": "2022-04-01T13:56:42Z",
  "published": "2022-04-01T13:56:42Z",
  "aliases": [ "CVE-2022-27651" ],
  "summary": "Non-empty default inheritable capabilities for linux container in Buildah",
  "details": "A bug was found in Buildah where containers were created ...",
  "affected": [
    {
      "package": {
        "ecosystem": "Go",
        "name": "github.com/containers/buildah"
      },
      "ranges": [
        {
          "type": "SEMVER",
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "1.25.0"
            }
          ]
        }
      ]
    }
  ],
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/containers/buildah/commit/..."
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/containers/buildah"
    }
  ]
}Data sources
This infrastructure serves as an aggregator of vulnerability databases that have adopted the OSV schema, including GitHub Security Advisories, PyPA, RustSec, and Global Security Database, and more.
Use the API
An easy-to-use API is available to query for all known vulnerabilities by either a commit hash, or a package version.
Query by commit hash
curl -d \
  '{"commit": "6879efc2c1596d11a6a6ad296f80063b558d5e0f"}' \
  "https://api.osv.dev/v1/query"
Query by version number
curl -d \
  '{"version": "2.4.1",
    "package": {"name": "jinja2", "ecosystem": "PyPI"}}' \
  "https://api.osv.dev/v1/query"
Vulnerability Scanner
Install OSV‑Scanner
go install github.com/google/osv-scanner/v2/cmd/osv-scanner@v2
Scan SBOM or Lockfiles
osv-scanner --sbom=cycloned-or-spdx-sbom.json
osv-scanner --lockfile=package-lock.json
Scan directory recursively
osv-scanner -r path/to/your/project
Remediation Tools
Guided Remediation (basic)
osv-scanner fix --non-interactive --strategy=in-place -L path/to/package-lock.json
osv-scanner fix --non-interactive --strategy=relock -M path/to/package.json -L path/to/package-lock.json
Guided Remediation (interactive)
osv-scanner fix -M path/to/package.json -L path/to/package-lock.json
Container Image Scanning
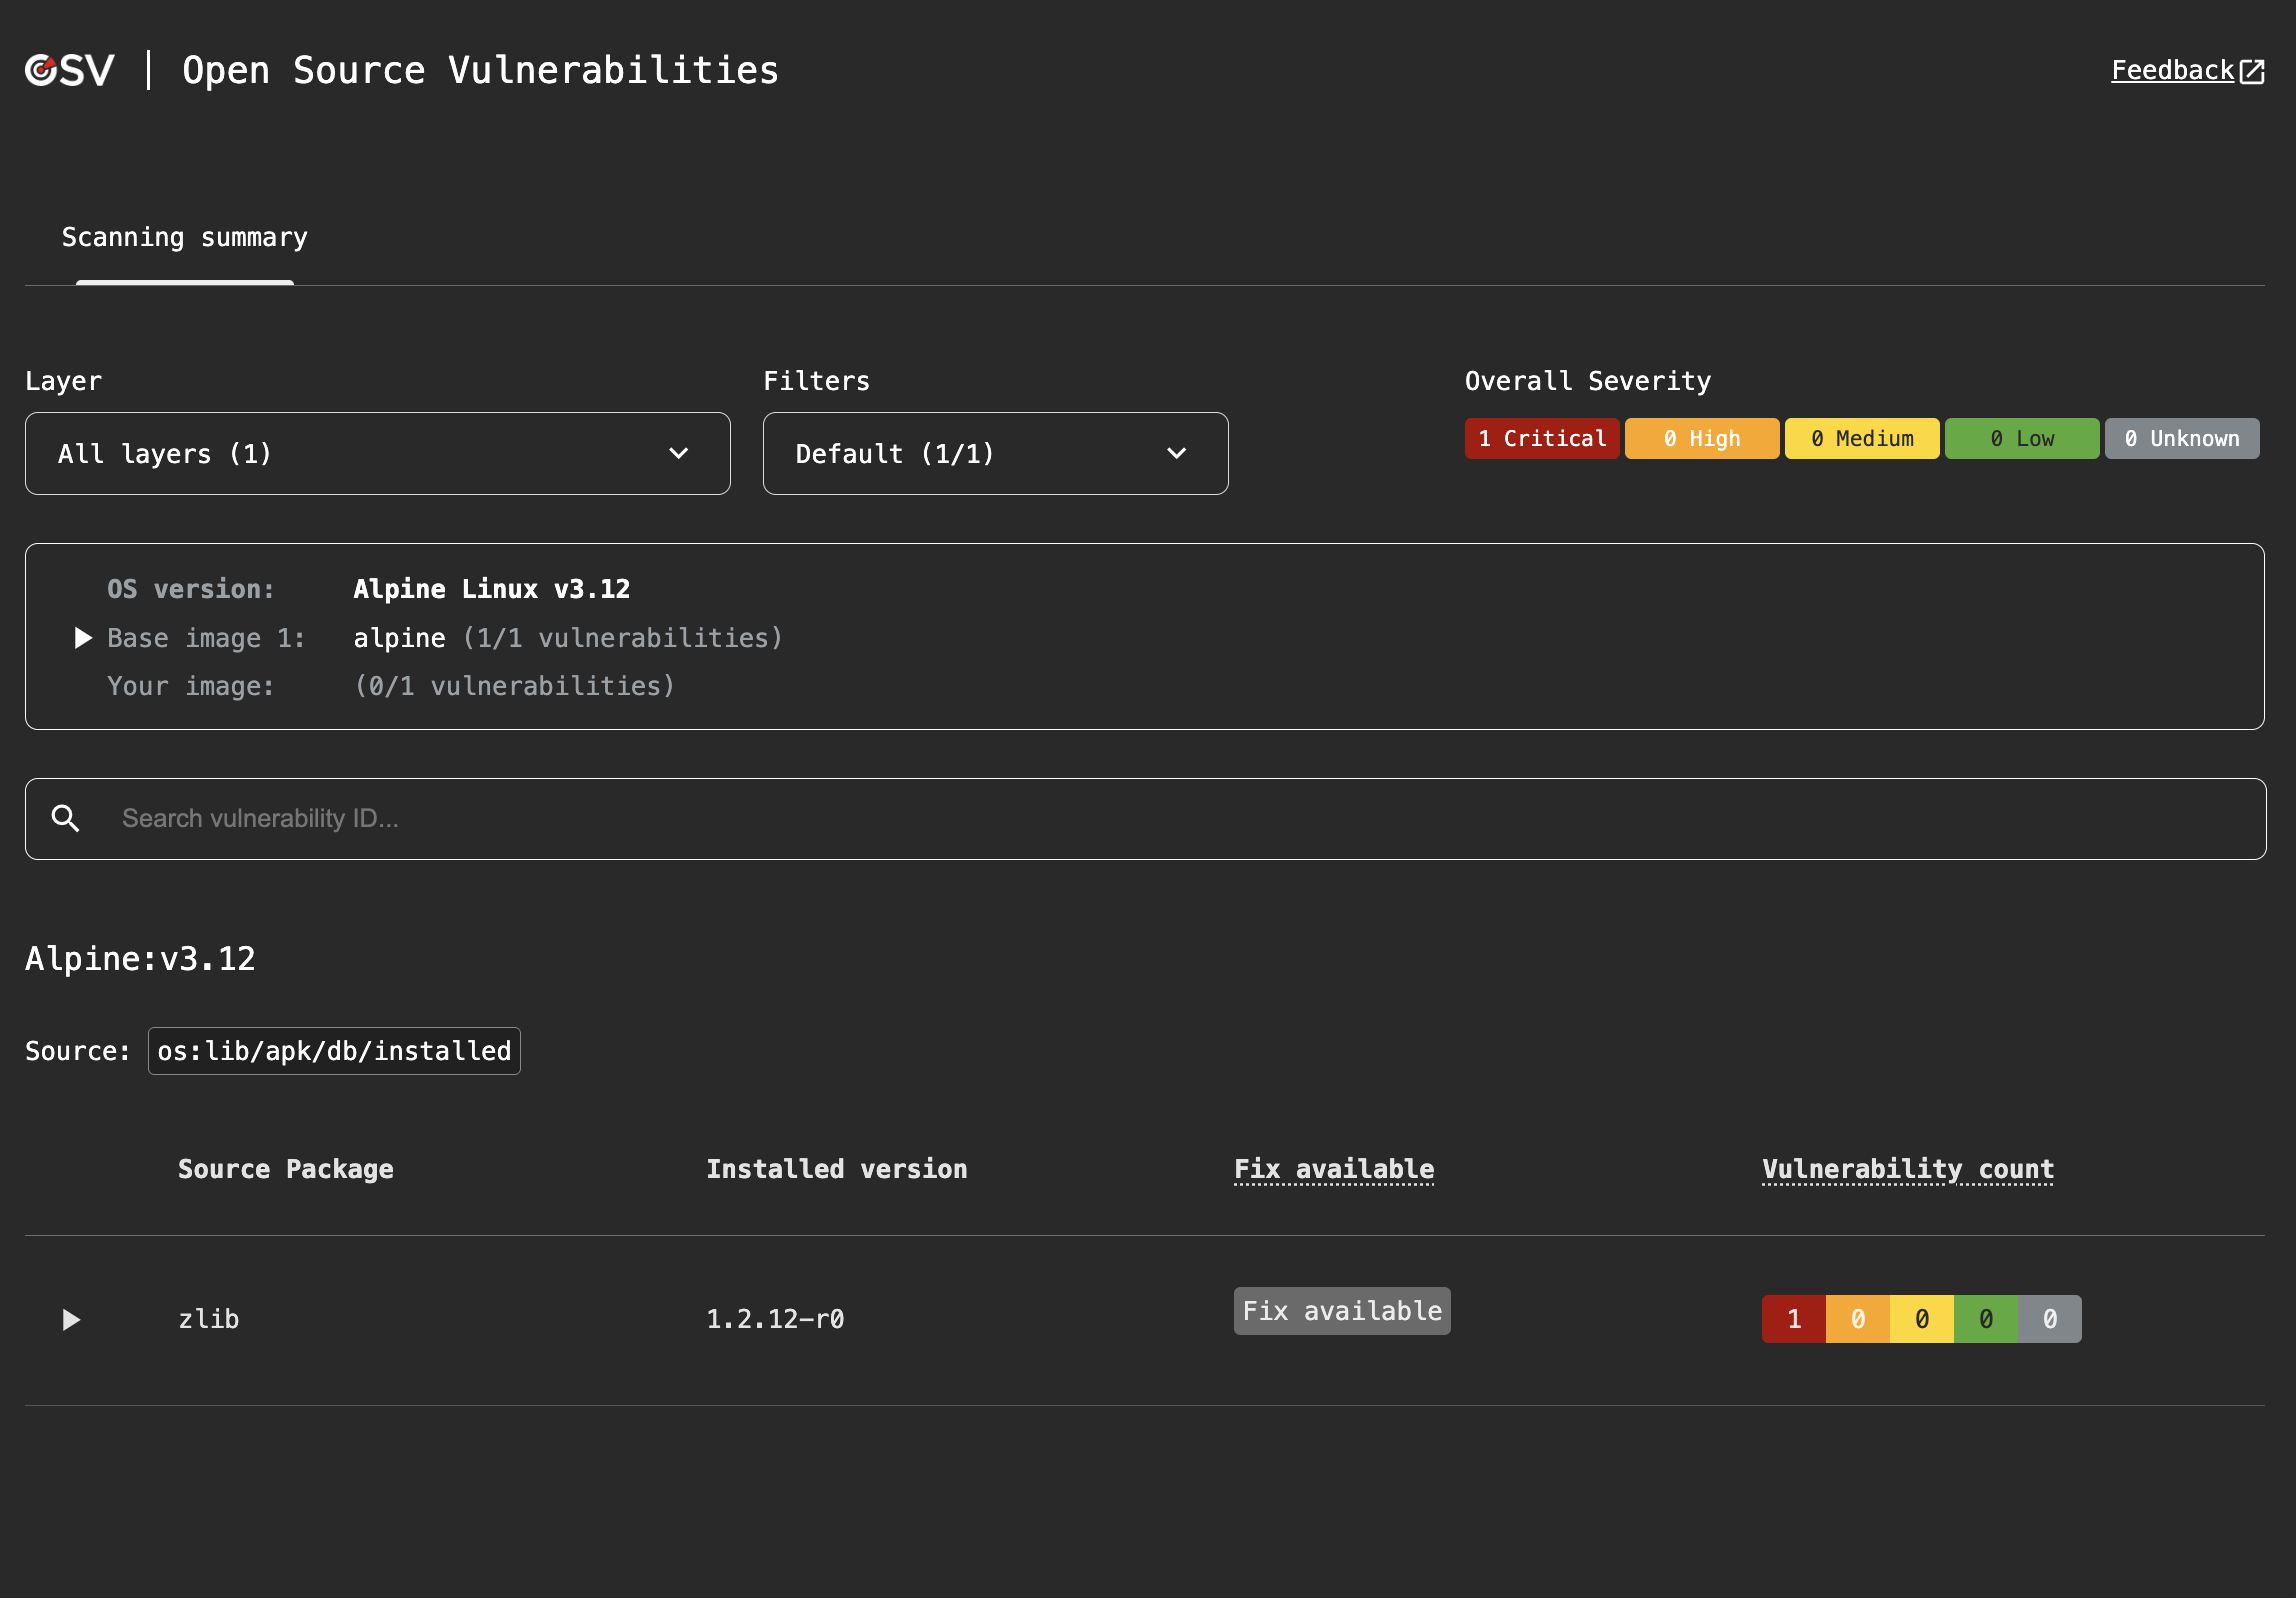
You can use OSV-Scanner to scan your container images for known vulnerabilities.
Scan container image
osv-scanner scan image --serve alpine:3.12
GitHub Workflows
OSV-Scanner also provides reusable GitHub workflows that can be easily integrated into CI/CD pipelines to provide continuous vulnerability scanning coverage. This can scan newly added dependencies in pull requests for introduced vulnerabilities, as well as perform regular vulnerability scans for the entire project.